Authority
Bind the AI agent identity, permitted action, resource, value, destination, time window and required approval.
Fidacy lets AI agents execute payments, refunds, customer operations, data workflows and production changes inside explicit, enforceable boundaries.
Define the right. Enforce it at execution. Prove the decision independently.
Works with the AI agents and frameworks your teams already run.
 Claude CodeNative plugin
 OpenClawNative plugin
 OpenAI AgentsNative adapter
 Vercel AI SDKNative middlewareCodexMCP host
 GitHub CopilotMCP host
 WindsurfMCP host
 Hermes AgentMCP + hooks
 OpenCodeMCP host
 ClineMCP host
 CrewAISDK / API
 PydanticAISDK / API
 Cloudflare AgentsSDK / API
 Strands AgentsSDK / API
 Microsoft Agent FrameworkSDK / API
 Google ADKSDK / API
 GrokBotAPI agent
Select an AI agent and a consequential action. Fidacy verifies identity, mandate, policy and request integrity before the connected executor receives permission to act.
Bind the AI agent identity, permitted action, resource, value, destination, time window and required approval.
Require a matching signed grant at the executor. No valid grant means no payment, email, export, refund or production change.
Sign every allow and deny, preserve the policy version and request digest, then anchor the evidence outside the operational system.
Show which AI agent actions are gated, observed, incomplete or outside control so security, legal and insurance teams see the real exposure.
Payments, supplier changes, data exports, credentials and production systems become attack paths when AI agent intent reaches them without an independent authority check.
Change the payee, amount, invoice or currency inside a workflow that already has payment access.
Export records, expose credentials or call production tools through permissions the organization granted itself.
Issue refunds, send commitments or change critical records before a human sees the consequence.
One production contract takes the highest-exposure AI agent actions from scope to enforcement, evidence and ongoing operation.
Identify AI agents, executors, actions, owners, approval thresholds and the consequences that require hard enforcement.
Require one matching grant before the protected system acts.
Track coverage, policy versions, approvals, evidence gaps and incident records.
Most products observe risk after an agent acts. Fidacy identifies the agent, verifies its mandate, enforces the boundary before execution and produces independently verifiable evidence after every decision.
Fidacy Firewall and Spend Guard refuse altered payees, excessive amounts, replayed grants and unauthorized side effects before the connected system is called.
KYA binds the workload identity. A signed mandate fixes the action, resource, amount, destination and duration. One matching request receives one executable grant.
Every ALLOW and DENY is signed. Continuous Control Monitoring shows whether the path was gated, merely observed, incomplete or outside current evidence.
Signed records enter append-only history, become Merkle checkpoints and receive an external Bitcoin timestamp that any third party can verify.
The action is only half the risk. Fidacy preserves neutral evidence of what moved, what was said and which exact artifact existed, without taking custody of the payment, transcript or file.
Bind payee, amount, invoice, currency and expiry. Where the payment rail is connected through Fidacy, an altered, excessive or replayed request is refused before settlement.
Hash each message locally, anchor the final session digest through Fidacy and give both sides a receipt they can verify. The transcript stays inside your infrastructure.
Anchor the hash of a prescription, insurance claim, contract, invoice, image or recording. Fidacy receives the digest, never the source file.
Fidacy does not price risk or issue policies. It gives underwriters a defensible view of which controls were operating, which actions were hard-gated, where coverage stopped and what happened in a specific incident.
Current boundaries, policy versions, connector state and evidence gaps.
Require hard-gated actions and current evidence for protected workflows.
Identity, mandate, signed decision, receipt, chain position and checkpoint.
Courts and regulators in four jurisdictions reached the same practical conclusion: an organization remains responsible for the automated action it deploys.
CONTROL COVERAGE · LIVE BOUNDARIESFidacy separates a hard gate from a heartbeat, current coverage from historical proof and a complete trail from a telemetry gap.
Fidacy is neutral to the model, agent framework, payment rail and system of record. The proof can be checked without calling us.
Decision, agent identity, governing mandate, policy version, receipt, chain position and external checkpoint in one portable package for the owner, auditor, insurer or regulator.
See the evidence package →Start through an SDK, MCP host or API. One compact layer fits the stack you already run while private prompts, files and tool arguments remain inside your environment.
One local server for agent tools and action boundaries.
npx -y @fidacy/mcpWrap the tool so a denied call never executes.
@fidacy/langchainEnforce between model intent and the external action.
@fidacy/openai-agentsObserve sessions, gate actions and export independent proof.
@fidacy/openclaw-pluginFidacy already implements the core authority chain in software: identity, signed mandates, pre-action decisions, enforceable grants, revocation and independently verifiable evidence.
Money · data · communications · enterprise systems
Already implemented at the software authority layer.
Gateway · device identity · local enforcement · safety validation
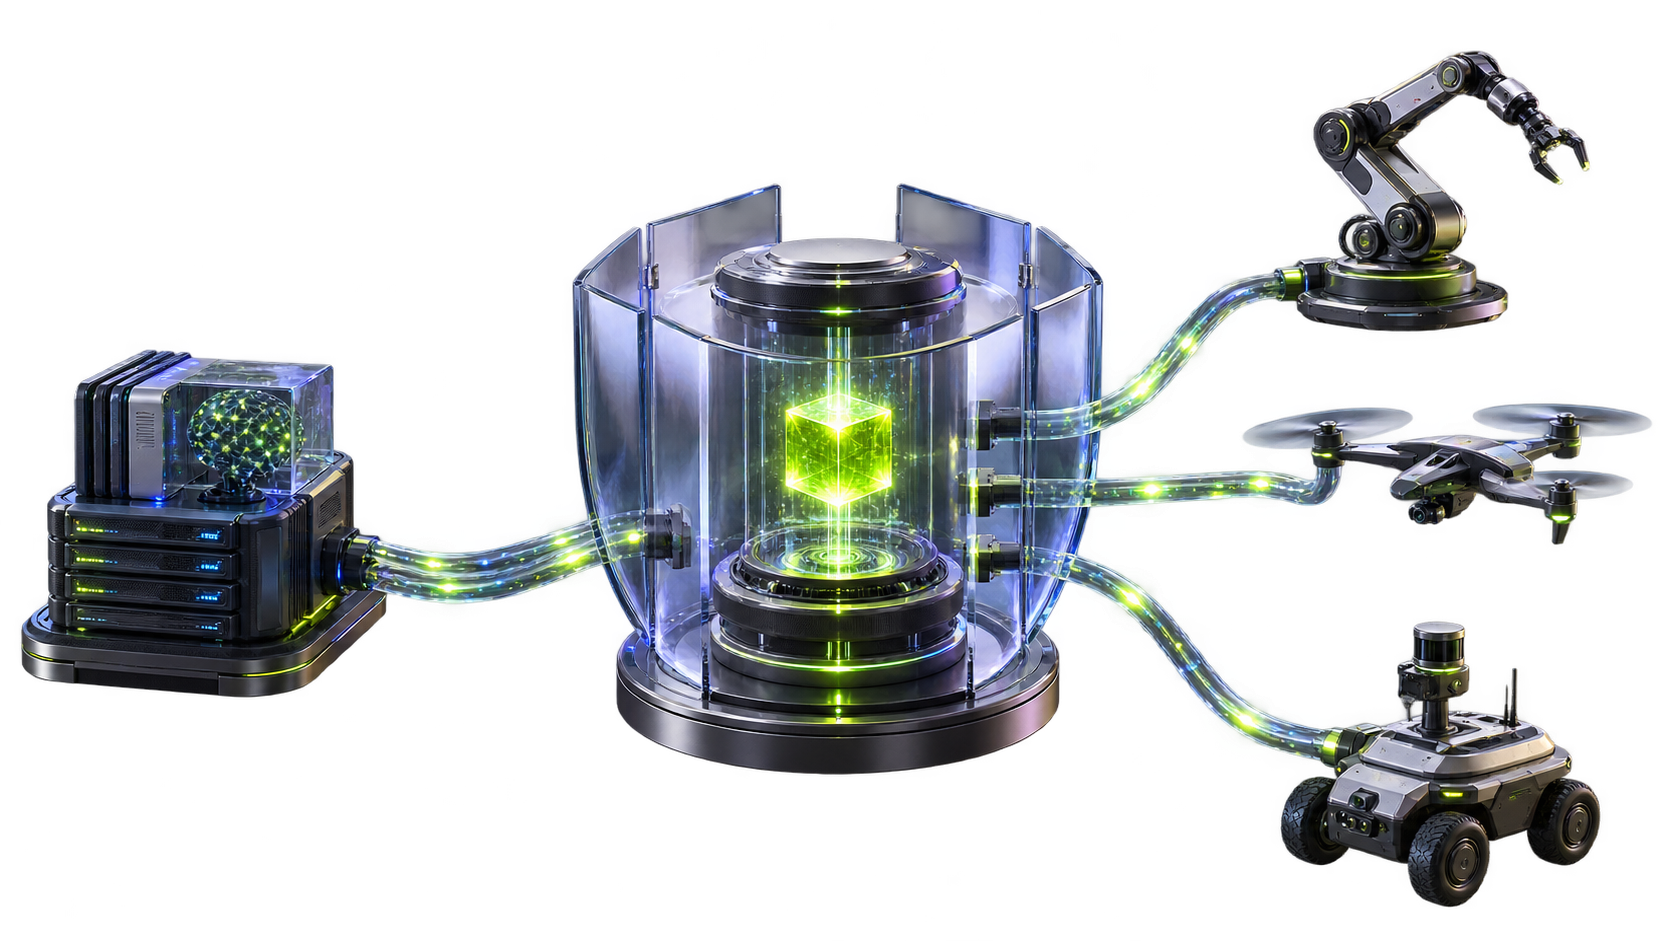
Mission-level authority for robots, drones, vehicles and safety-critical autonomous infrastructure, without entering the motor-control loop.
≈90% is an architecture-reuse estimate, not physical-product readiness or safety certification.
Intelligence decides what to do.Authority decides whether it may happen.
European Commission AI Pact, Pillar I. Singapore Model AI Governance Framework. Fidacy contributes implementation practices for trustworthy AI and AI Act readiness.
 PUBLIC POLICY CONTRIBUTION · 2026
SINGAPORE
Fidacy submitted a production-backed enforcement case study to Singapore's Model AI Governance Framework for Agentic AI consultation.
Read the technical contribution → AI PACT · PILLAR I · 2026
EUROPEAN COMMISSION
Fidacy has joined Pillar I, contributing implementation practices for trustworthy AI and AI Act readiness.
View the AI Pact →Map the exposed actions, define signed authority and leave with a deployment scope for your AI agents, executors, policies and evidence requirements.